SaaS · REAP Cloud
- Available today; quick start and time to value
- Fully managed, always current
- AWS (opens in a new tab), U.S. regions; tenant isolation enforced at the application layer
- Connector cluster (agent + proxy) inside your network
Architecture & deployment
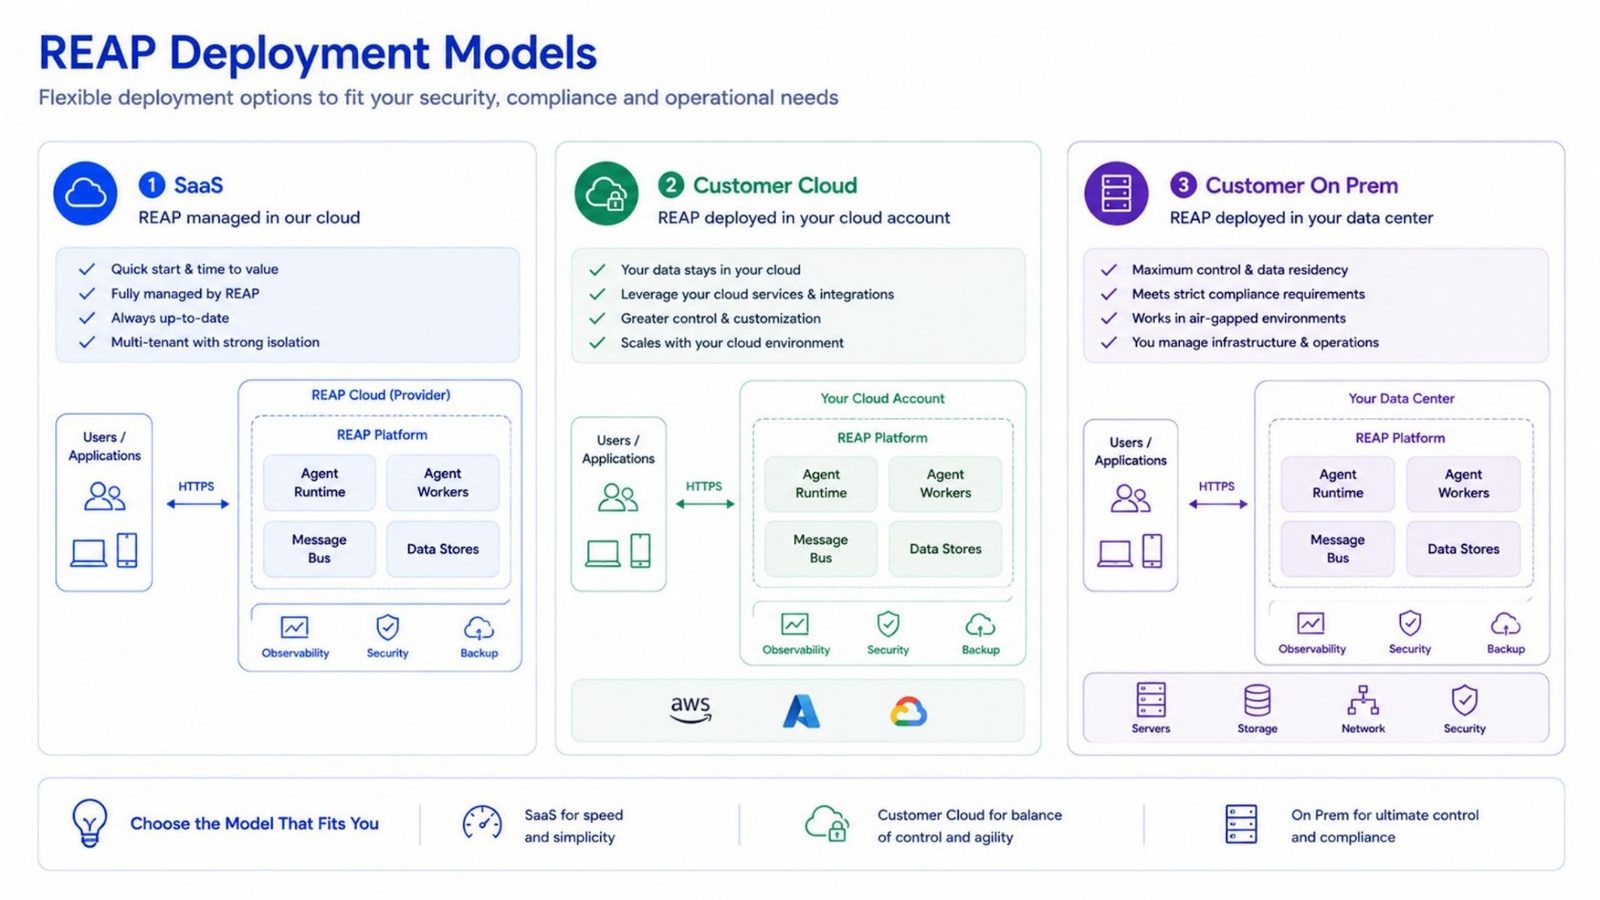
SaaS runs today. Your own cloud account for residency, or on-premises for maximum control, are available by arrangement and scoped per customer. In every model a connector cluster inside your network handles collection with read-only credentials, brokered through CyberArk (opens in a new tab) where available.
Deployment models
The connector cluster
A connector cluster runs inside your network and is the only thing that touches your devices. It collects configurations, state and telemetry with read-only credentials, brokered through your privileged-access system where available, and opens an outbound TLS connection to REAP, so no inbound firewall rule is needed. You can revoke its access at any time. Ports, encryption and the data classes collected are documented in the security packet, under NDA.
Multi-tenant SaaS
Authentication and role-based access, multi-tenancy, alerting, scheduling and audit logging are platform services shared by every deployment model. In REAP Cloud, tenants are isolated with access enforced at the application layer; SSO (SAML/OIDC) with your identity provider is supported.
Data classes collected, retention, deletion, model-endpoint options and the model-training policy are answered in writing in the security packet rather than summarized here.
Most pilots run in REAP Cloud with read-only access. Where policy requires your own AWS (opens in a new tab), Azure (opens in a new tab) or GCP (opens in a new tab) account, the deployment is scoped with your cloud and identity teams and its timeline agreed before week 0.